Agentic Dev Team


Three Claude Code plugins for engineering workflows. Install one or all.
dev-teamgives Claude Code a full persona-driven development team. It includes an Orchestrator that routes tasks, specialist agents (engineer, QA, architect, reviewers…), skills that encode reusable knowledge, and the four-command feature workflow/specs → /plan → /build → /pr.security-assessmentis the security companion. It adds a tool-first/security-assessmentpipeline (SAST + AI judgment + false-positive filtering + executive report), a/cross-repo-analysiscommand for multi-repo attack chains, and an adversarial ML red-team harness (/redteam-model) for self-owned model endpoints.marketplace-devis the plugin-author's toolkit. It scaffolds new plugins and marketplaces (/scaffold-plugin,/scaffold-marketplace,/init-plugin-eval). It audits any plugin for structural compliance (/plugin-audit). It advises on the markdown-vs-script agent decision (/agent-type-advisor). It also ships the migrated agent/skill authoring toolkit (/agent-create,/agent-add,/agent-remove).
dev-team is the foundation. It owns the shared data contract (codebase-recon, ACCEPTED-RISKS.md, unified finding format) that security-assessment builds on. Install dev-team first, and add security-assessment when you need it. marketplace-dev is independent. It has no hard dependency on dev-team, so you can install it on its own to build or maintain plugins.
Plugins
| Plugin | What it does | Key commands | Required tools | Optional tools |
|---|---|---|---|---|
| dev-team | Persona-driven development team, reviewer swarm, TDD-gated build loop | /specs, /plan, /build, /pr, /code-review, /triage |
jq, gh |
semgrep, playwright, hadolint/trivy/grype; auto-detected formatters and test/type/lint runners |
| security-assessment | Tool-first security assessment + red-team pipeline | /security-assessment, /cross-repo-analysis, /redteam-model, /export-pdf |
dev-team, Python ≥ 3.10, tier-1 SAST (semgrep, gitleaks, trivy, hadolint, actionlint) |
grype, PDF-export deps |
| marketplace-dev | Scaffold, audit, and maintain Claude Code plugins and marketplaces | /scaffold-plugin, /scaffold-marketplace, /plugin-audit, /agent-type-advisor, /agent-create |
jq |
git |
Plugin names link to each plugin's README, where the full tool list and per-tool install commands live. This table assumes you have Claude Code. First time here? Start with dev-team. Add security-assessment only when you run full /security-assessment pipelines against target repos. Add marketplace-dev when you build or maintain plugins.
Getting started
New here? The Getting Started guide is the full walkthrough. It covers installing each plugin, configuring a project, the day-to-day workflow, and the diagnostic commands.
Quick install of the core plugin:
Then run /setup in your project. The Getting Started guide covers the optional plugins (security-assessment, marketplace-dev), self-hosted git hosts, install scopes, and the /upgrade flow.
Dev team workflow
Four commands drive feature development from idea to pull request:
| Step | Command | What it does |
|---|---|---|
| 1. Specify | /specs |
Describe the change and its goals — Intent, Architecture notes, Acceptance Criteria. A consistency gate must pass before you move on. Skip for bug fixes, refactors, or trivial changes. |
| 2. Plan | /plan |
Decompose the feature into vertical slices, author each slice's Gherkin scenarios, and lay out the TDD steps that satisfy them. Up to five plan-review personas (Acceptance Test, Design, UX, Strategic, Parallelization critics), scaled to the plan tier, challenge the plan before the human sees it. The human approves before any code is written. |
| 3. Build | /build |
Execute the approved plan slice by slice. Each step follows RED-GREEN-REFACTOR with inline review checkpoints (spec-compliance first, then quality agents). It produces verification evidence. |
| 4. Ship | /pr |
Run quality gates (tests, typecheck, lint, code review) and open a pull request. |
Each step produces artifacts that the next step consumes. The spec describes what and why. The plan turns the spec into per-slice behavioral contracts (Gherkin) and how. Human review gates sit between transitions.
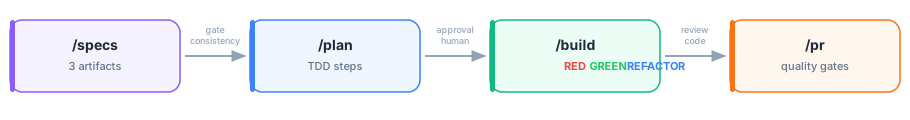
For bug fixes or simple tasks, skip /specs and start at /plan, or go straight to implementation.
Supporting commands
The table below lists representative supporting commands. For the full catalog with options and descriptions, see the skills page of each plugin: dev-team skills · security-assessment skills · marketplace-dev skills.
| Command | Plugin | When to use |
|---|---|---|
/code-review |
dev-team | Run review agents, auto-fix actionable issues, re-run until clean (up to 5 iterations) |
/continue |
dev-team | Resume an in-progress build or plan across sessions |
/test-improve |
dev-team | Consolidated analyze-then-improve test orchestrator. Ten phases (0-9) with human gates. Lightweight by default. Opt into Gherkin / mutation / refactor-for-testability on demand |
/browse |
dev-team | Visual QA via Playwright |
/benchmark |
dev-team | Runtime performance metrics (Core Web Vitals, resource sizes) against baselines |
/careful / /freeze / /guard |
dev-team | Safety modes for production-critical sessions |
/triage |
dev-team | Investigate a bug and file a GitHub issue with a TDD fix plan |
/security-assessment |
security-assessment | Full pipeline: recon → tools → agents → FP-reduction → exec report |
/redteam-model |
security-assessment | Adversarial ML red-team probes against a self-owned model endpoint |
/plugin-audit |
marketplace-dev | Structural compliance check for any Claude Code plugin |
/scaffold-plugin |
marketplace-dev | Create a new plugin skeleton that passes audit with zero findings |
Automated pre-commit review
/code-review automatically gates every git commit. A PreToolUse hook detects commit attempts and blocks them until a passing review exists for the exact set of staged files.
Flow: attempt commit → hook blocks → Claude runs /code-review → if pass/warn, Claude writes a .review-passed gate file → next commit attempt succeeds.
Bypass: git commit --no-verify skips the review gate.
Security assessment pipeline
/security-assessment <path> runs a six-phase pipeline against one or more target repos. Deterministic tools do the detection. LLM agents handle the judgment stages.
| Phase | Runs | Output |
|---|---|---|
| 0. Recon | codebase-recon agent |
memory/recon-<slug>.{json,md} |
| 1. Tool-first detection | semgrep, gitleaks, trivy, hadolint, actionlint, custom rulesets | unified findings stream |
| 1b. Judgment | security-review, business-logic-domain-review agents |
appended findings |
| 1c. Suppression | ACCEPTED-RISKS.md gate (deterministic) |
filtered stream + audit log |
| 2. False-positive filter | 5-stage check (reachability, environment, controls, dedup, severity) | decisions log |
| 2b. Severity floors | deterministic domain-class calibration | floor-adjusted scores |
| 3. Narrative + compliance | tool-finding-narrative-annotator, compliance-mapping skill |
4-domain narrative + compliance JSON |
| 4. Cross-repo | service-comm parser, shared-cred hash match (multi-target only) | mermaid diagram + SARIF |
| 5. Exec report | exec-report-generator agent |
publication-ready 7-section markdown |
Zero-install flow: scripts/run-assessment-local.sh runs the same pipeline from the repo checkout without installing the plugin. The script auto-detects the claude CLI and degrades to deterministic-only when the CLI is absent. See the user guide for the full runbook.
Adversarial ML red-team: /redteam-model probes a self-owned model endpoint (localhost / private network by default; public targets require a signed authorization.md). Eight probes cover discovery, evasion, data extraction, and report synthesis.
Contributing
Developing, testing, or releasing the plugins? See CONTRIBUTING.md. It covers local-dev setup (including live installs via symlinks), the /agent-eval and /agent-audit test commands, the security comparative-testing harness, how to add agents and skills, and the release process.
/code-review benchmark harness (evals/code-review-benchmark/): checks out real, known-defect commits from Defects4J (Java) and BugsJS (JavaScript), runs /code-review against the buggy revision, and scores whether its findings cover the real defect. The harness also produces a dedicated Missed Defects report. Adapters and scoring are unit-tested against real fetched dataset samples. A live sweep against the actual corpora requires a local Defects4J/BugsJS install (see the harness README for prerequisites and usage).
Documentation
The full documentation lives at devteam.bryanfinster.com, with search and complete navigation. It covers architecture, model routing, the eval system, telemetry, ADRs, and experiment reports.
Start here:
| Doc | Covers |
|---|---|
| Getting Started | Install, the workflow, suggested skills, worked examples |
| Contributing | Local development, testing, adding agents/skills, releasing |
| Plugin Development Guide | Project North Star, repo structure, working rules |
Per-plugin docs: dev-team · security-assessment · marketplace-dev. Each plugin's README is the entry point to its architecture, commands, and deeper guides.
CodeGraph
This repository uses CodeGraph for semantic code intelligence.